Last updated 18 November 2026: updated Vinyl’s answers on storage, retention, deletion, breach notice and staff access.Last updated November 18, 2026: updated Vinyl’s answers on storage, retention, deletion, breach notice and staff access.
Yes, an AI notetaker is safe to use in client meetings when your firm gets consent, the tool protects and doesn’t train on client data, and a person reviews the summary before it goes on the file. Here is the checklist we’d use to judge any notetaker, including ours.
Quick verdict
- Consent: your firm’s job, not the vendor’s. Tell people the meeting is recorded, in the invite and at the start of the call.
- Security: look for encryption in transit (TLS 1.2+) and at rest (AES-256), access controls and two-step sign-in.
- AI training: the answer you want is a clear no. Vinyl doesn’t train AI on your meetings.
- Data location: know where data is stored and where it is processed. Vinyl keeps the lasting copy of every meeting on AWS in Sydney.
- Accuracy: review important figures and decisions before relying on the summary.
- Comparing tools: see our AI meeting assistant for accounting firms comparison.
Key points:
- Firms should inform participants and obtain any consent required before recording client meetings
- Sensitive client data should be protected with strong encryption, access controls, multi-factor authentication, and clear deletion policies
- Accounting firms should confirm that recordings, transcripts, and summaries are not used to train AI models
- Firms need to understand where meeting data is stored and processed, especially when regulatory or residency requirements apply
- AI-generated notes are not perfectly accurate, so important financial figures, decisions, and actions should be reviewed by a human
- Purpose-built accounting notetakers can provide better terminology recognition, speaker identification, and structured client records than generic tools
- Securely storing approved meeting records alongside existing practice management systems can strengthen documentation and reduce reliance on handwritten notes or memory
Being cautious about recording client conversations is the right instinct.
Accounting firms handle financial records, tax information, payroll data and personal details that clients expect to remain confidential. An AI notetaker should therefore never be adopted simply because it saves time.
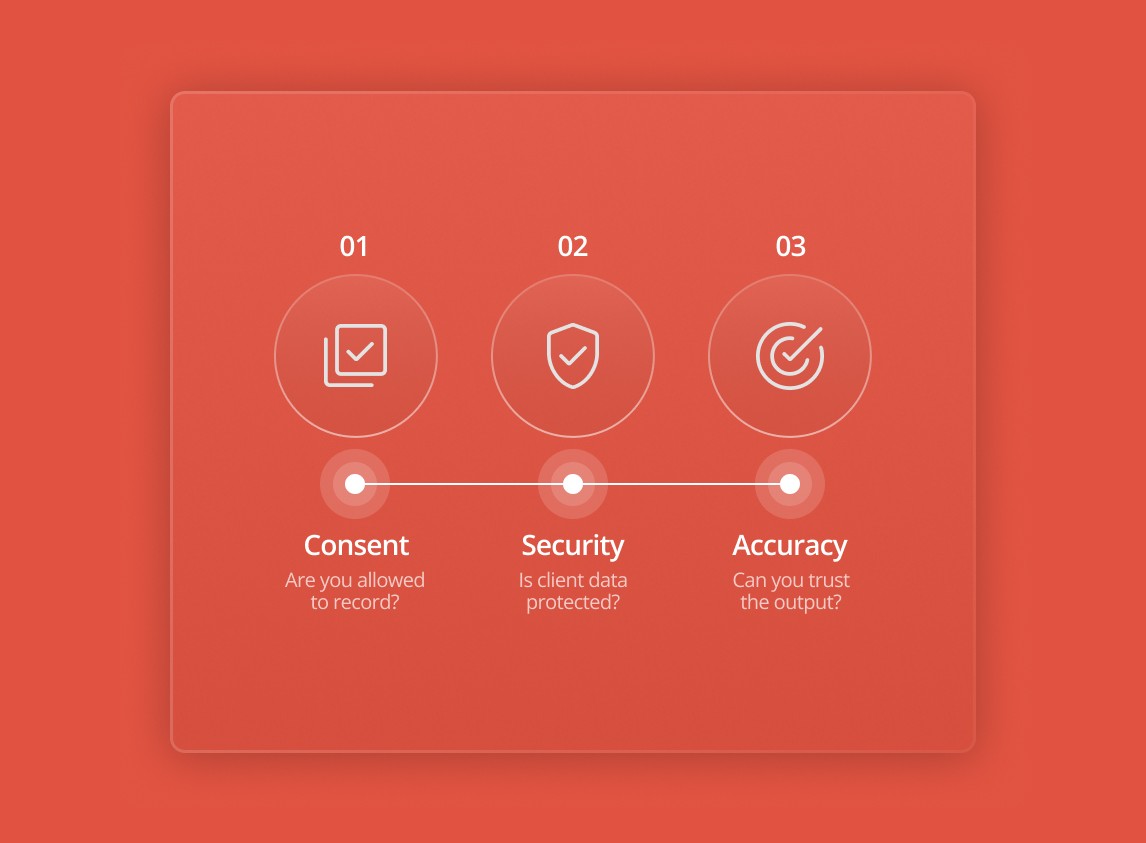
But “Is it safe to use an AI notetaker?” is not really one question.
It is three:
- Are you allowed to record the meeting?
- Is the client data secure after it has been captured?
- Can you trust what the AI produces?
A tool can meet one of those requirements and still fail another. Encryption does not remove the need for consent, and a clear recording notice does not guarantee an accurate summary.
The choice is also broader than “AI notetaker or no notetaker.” Many firms already rely on handwritten notes, personal recording devices, summaries typed from memory or generic consumer tools with limited controls. Meeting information is often scattered across inboxes, notebooks, and individual devices.
A purpose-built AI notetaker can be the safer option when your firm handles consent properly, chooses a vendor with credible security and privacy practices, and treats the output as a reviewable record rather than unquestionable truth.
As Cameo Ashe of Lemonade Beach Accounting said: “I’ve been wary of AI notetakers in the past… but Vinyl just gets it.”
That wariness is healthy. The goal is to turn it into a practical checklist for evaluating any tool your firm considers.
Is it legal to record a client meeting?
Recording laws vary between countries, states and other jurisdictions.
Some follow one-party consent rules, under which one participant may be permitted to record the conversation. Others require every participant to be informed or to give explicit consent.
Your firm is responsible for understanding the rules that apply to its location and the locations of meeting participants. As such, please keep in mind that in this article we offer general guidance, not legal advice.
The safest practical habit is straightforward: tell people when a meeting is being recorded.
Consent is the firm’s responsibility, not the software provider’s. The notetaker captures the conversation, but your firm owns the disclosure and the decision to proceed.
This does not need to become an awkward legal script. Add a short notice to the calendar invitation and repeat it at the beginning of the call: “We use an AI meeting assistant to record and summarise our calls so we can maintain an accurate record. Is everyone comfortable with that?”This does not need to become an awkward legal script. Add a short notice to the calendar invitation and repeat it at the beginning of the call: “We use an AI meeting assistant to record and summarize our calls so we can maintain an accurate record. Is everyone comfortable with that?”
Clients are increasingly familiar with recorded calls. Explaining that the purpose is more accurate documentation and reliable follow-up usually makes the process easier.
The same requirement applies outside Zoom or Teams. When using the Vinyl mobile app to capture an in-person or telephone meeting, participants still need to be informed and consent obtained where required.
The tool itself should support transparency. A safe notetaker joins online meetings visibly, with a recognisable name and image, rather than recording silently. Your team should also be able to control whether it attends a particular meeting.The tool itself should support transparency. A safe notetaker joins online meetings visibly, with a recognizable name and image, rather than recording silently. Your team should also be able to control whether it attends a particular meeting.
Vinyl appears visibly in Zoom, Microsoft Teams and Google Meet calls, and provides recording-notification templates. However, obtaining the appropriate consent remains your firm’s responsibility.
Creating a consistent approach to consent and proper documentation is safer than leaving each team member to improvise the process.
Is client data actually secure?
Once consent has been addressed, the next question is what happens to the data.
Accounting firms hold some of their clients’ most sensitive information. Any AI notetaker should therefore be able to explain clearly how recordings, transcripts, summaries and account data are protected.
Before adopting a tool, every firm should ask these questions:
- Is data encrypted in transit and at rest?
- Where is it stored and processed?
- Who can access each meeting?
- Can vendor employees view the content?
- Is multi-factor authentication available?
- Is client data used to train AI models?
- What security standards support the infrastructure?
- Is a Data Processing Agreement available?
- What happens when a meeting or account is deleted?
A vague claim of “industry-standard security” is not enough. Your compliance team should be able to find specific, published answers.
1. Encryption
A secure AI meeting assistant should encrypt data throughout its lifecycle.
Encryption in transit protects information as it moves between the meeting platform, your browser, the vendor and its service providers. Look for TLS 1.2 or higher.
Encryption at rest protects stored recordings, transcripts and summaries. AES-256 is the standard firms should expect for confidential meeting information.
Vinyl uses TLS 1.2+ in transit and AES-256 at rest.
2. Access controls
Not every member of your firm should automatically see every meeting.
A routine client review, an internal performance conversation, and a partner discussion have different access requirements. Look for role-based permissions, multi-factor authentication and sharing controls that allow records to remain private or be shared only with selected people.
The vendor should also explain whether its own employees can access meeting content. Access should be limited to tightly controlled circumstances, such as resolving a specific support request.
3. AI model training
Ask every vendor directly whether customer recordings, transcripts or summaries are used to train its AI models.
The answer you want is a clear no.
At Vinyl, customer meeting content is not used for AI training. It is processed only to provide the transcription, summarisation and workflow services requested by the firm.At Vinyl, customer meeting content is not used for AI training. It is processed only to provide the transcription, summarization and workflow services requested by the firm.
Client conversations should not become general training material for a vendor’s future products.
4. Infrastructure and compliance
Certifications do not make a platform risk-free, but they demonstrate that the underlying infrastructure is subject to recognised controls.Certifications do not make a platform risk-free, but they demonstrate that the underlying infrastructure is subject to recognized controls.
Vinyl runs on AWS, which is certified to ISO 27001 and SOC 1, 2 and 3. Those are AWS’s certifications, not Vinyl’s own. If a breach affects your firm’s data, Vinyl will tell you within 48 hours of becoming aware of it.
Vinyl’s Data Processing Agreement covers the Australian Privacy Act and the UK GDPR. Firms can ask for a copy.
These safeguards are detailed in the Vinyl Privacy & Security FAQ.
5. Data location and processing
Your firm should know both where data is stored and where it is processed.
Vinyl keeps the lasting copy of every recording, transcript, summary and file note on AWS in Sydney, and the AI behind Vinyl Studio runs on AWS in Australia. Recording and speech to text use specialist providers in the United States, and speaker separation runs in the European Union. Those providers return their results to Australia and delete their working copies within 30 days. Vinyl names them on request.
That distinction matters for firms with GDPR requirements or clients who ask about data residency. Clear disclosure allows you to evaluate and document the arrangement rather than discovering it after implementation. If you run a UK practice, our guide to choosing an AI notetaker for UK accountants covers the data questions a UK firm should ask.
6. Deletion
Security includes the end of the data lifecycle.
Vinyl keeps meeting records for up to seven years by default, or less if your firm asks. You can delete a meeting whenever you like, or ask Vinyl to delete your firm’s records sooner. If you leave, you choose a full copy of your data in a standard format, deletion, or both, and Vinyl confirms in writing once it’s done. Backups age out within 30 days.
A defined deletion process is safer than allowing confidential recordings to remain indefinitely on personal devices, shared drives or disconnected applications.
Can you trust what the AI writes down?
Security is not the only form of safety.
A summary that quietly gets a tax figure, deadline, decision or speaker wrong can create its own risk. This matters when the meeting record may later be used to confirm what your firm recommended or what the client agreed to do.
No transcription tool is 100% accurate.
Vinyl’s typical transcription accuracy is roughly 95%, depending on audio quality, accents, background noise, overlapping speakers and terminology.
That is not a reason to avoid AI notes. It is a reason to set the correct expectation and retain human review.
Generic notetakers often struggle with accounting language because they are designed for every kind of meeting. They may mishear tax, payroll, trust or compliance terminology, miss one critical line in a long discussion, or attribute a statement to the wrong person.
For an accounting firm, trustworthy output should provide:
- correct speaker attribution;
- clear decisions and deadlines;
- separate client and firm actions;
- accurate accounting terminology;
- a structured summary that absent colleagues can understand;
- access to the transcript and recording for verification.
Vinyl is designed around accounting conversations and reports approximately 95% terminology accuracy. Voiceprint Speaker Identification helps distinguish who said what, while structured summaries separate decisions, client actions and firm actions.
The workflow still matters more than any accuracy percentage.
Important summaries should be reviewed before they are treated as final. Client-facing email drafts and other dynamic post-meeting actions should remain editable and should not be sent without approval.
The original recording should also remain available as the source record. When a number, commitment or recommendation needs to be checked, your team can return to the actual conversation rather than relying entirely on a generated summary.
This is the practical answer to whether AI meeting summaries are accurate enough for financial discussions. They can support the client record when the tool understands accounting vocabulary, identifies speakers correctly, and makes verification easy.
It also explains why generic Zoom, Teams and Google Meet notetakers fall short for accounting firms. Producing a transcript is not the same as creating a structured and defensible accounting record.
A recorded meeting can be the safer option
The instinctive concern is that recording a meeting creates more exposure.
In some situations, the greater risk is having no reliable record at all.
Handwritten notes, delayed summaries and actions buried in inboxes can all weaken the client record. Important nuance may be lost, recollections may replace the exact wording of the conversation, and next steps can become separated from the reasoning behind them. By the time a client, colleague or regulator asks what was advised or agreed, the firm may be left piecing together fragments.
That is becoming harder to justify as professional expectations across key markets move towards stronger, more demonstrable documentation. In Australia, the TPB Code Determination 2024 strengthened record-keeping and false or misleading statement obligations for most firms from 1 July 2025. In the UK, both the failure-to-prevent-fraud offence and HMRC’s minimum-standards regime place greater value on firms being able to evidence the procedures they followed. In the United States, revised AICPA Statements on Standards for Tax Services and proposed Circular 230 updates point in the same direction by reinforcing the importance of documented advice and data security.That is becoming harder to justify as professional expectations across key markets move toward stronger, more demonstrable documentation. In Australia, the TPB Code Determination 2024 strengthened record-keeping and false or misleading statement obligations for most firms from July 1, 2025. In the UK, both the failure-to-prevent-fraud offense and HMRC’s minimum-standards regime place greater value on firms being able to evidence the procedures they followed. In the United States, revised AICPA Statements on Standards for Tax Services and proposed Circular 230 updates point in the same direction by reinforcing the importance of documented advice and data security.
These examples are general context rather than legal advice, but the broader trend is clear: firms are increasingly expected to show what was advised, agreed and completed. A searchable, timestamped meeting record can make that much easier.
The documentation and security questions must work together. A recording is only useful when it is securely stored, deliberately shared and connected to the systems where your firm already controls access.
Records are less safe when they remain in an employee’s notebook, inbox or standalone recording account. An approved meeting summary should flow into the practice management environment alongside the rest of the client history.
Vinyl supports two-way syncing with Karbon and FYI, along with a one-way client and contact pull from Xero Practice Manager. These integrations allow meeting context to live beside the existing client record instead of in a separate silo.
Its Smart Share controls help teams decide what remains private, what is shared internally, and what can be shared with selected clients or other participants.
Used properly, an AI notetaker becomes a form of compliance insurance that also saves time. It creates a fuller record while reducing the manual work that causes documentation to be delayed, incomplete or forgotten.
Safety is a choice your firm makes
No AI notetaker is automatically safe, and no responsible vendor should promise zero risk.
Safety comes from the decisions around the tool:
- inform participants and obtain the consent required;
- insist on published security and privacy credentials;
- confirm that client data is not used for model training;
- understand where information is stored and processed;
- control access to each meeting;
- review important summaries before relying on them;
- retain the recording for verification;
- connect approved records to systems where access is already governed.
Use that checklist for any AI notetaker your firm is considering, including tools individual employees may already be using informally. For a wider view of where firms are putting AI to work, see what our survey of 259 accounting firms found.
When those conditions are met, the answer to “Is it safe to use an AI notetaker in client meetings?” can be yes.
Vinyl was built for accounting firms that are right to be wary. You can start a free trial to test it with your own meetings or book a 15-minute demo to discuss your firm’s security, consent and integration requirements.
Frequently Asked Questions
Is it safe to use an AI notetaker in client meetings?
Yes when you handle it properly. That means informing participants and getting consent as your jurisdiction requires, choosing a tool with real security credentials (encryption, access controls, reputable infrastructure), and reviewing important AI summaries before relying on them. The risk comes from generic consumer tools and skipped consent, not from AI notetakers as a category.
Do I need consent to record a client meeting?
In most cases yes. Many jurisdictions require you to inform participants, and some require explicit consent, before recording. Obtaining that consent is the firm’s responsibility. A short verbal notice at the start of the call plus a line in the calendar invite is usually enough. This is general guidance, not legal advice, so check the rules that apply to you.
Is my client data secure with an AI meeting assistant?
It depends entirely on the tool. Look for encryption in transit (TLS 1.2+) and at rest (AES-256), multi-factor authentication, role-based access, and infrastructure that meets standards like ISO 27001 and SOC 2. Vinyl uses TLS 1.2+ and AES-256, offers two-step verification with an authenticator app and roles for your firm, and runs on AWS, which is certified to ISO 27001 and SOC 1, 2 and 3.
Will an AI notetaker use my meetings to train its AI models?
It should not, and you should confirm this before adopting any tool. Vinyl does not use your recordings, transcripts or summaries to train its AI. Your content is used only to deliver the service you asked for.
How accurate are AI meeting summaries for financial conversations?
Transcription accuracy typically runs 85-95%, depending on audio quality, accents and terminology, so important summaries should always be reviewed. Tools built for accounting handle financial vocabulary and speaker attribution far better than generic notetakers, which makes their summaries safer to rely on for the client record.
Where is my data stored when I use Vinyl?
The lasting copy of every recording, transcript, summary and file note is stored on AWS in Sydney, and the AI behind Vinyl Studio runs on AWS in Australia. Recording, transcription and speaker separation use providers in the United States and the European Union, which return their results to Australia and delete their copies within 30 days. Vinyl’s Data Processing Agreement covers the Australian Privacy Act and the UK GDPR, and firms can ask for a copy.
What admin controls should IT ask for before approving an AI notetaker?
Ask for control over who has an account, two-step sign-in, sharing that is private by default, the ability to delete a meeting, and a clear answer on whether vendor staff can see content. In Vinyl, admins manage the firm’s team, staff can sign in with Google or Xero, Smart Share decides what is shared and with whom, and individual meetings can be deleted. The Privacy & Security FAQ lists the rest.
Can we keep a sensitive client meeting from the rest of the firm?
Yes. With Smart Share on, a meeting that includes anyone outside your firm is visible to your whole team, and a meeting with only your own people stays private by default. For a client conversation that shouldn’t be seen widely, such as a family matter or a partner leaving the business, you can control sharing for that meeting by hand. Decide your firm’s rule for these meetings before the first one comes up.
Can a client ask us to delete the recording?
Yes. You can delete an individual meeting in Vinyl. If the summary was also filed to the client’s record in Karbon or FYI, remove that copy there too, because it’s now part of your practice management record. Agree in advance who in the firm handles these requests, so a client gets the same answer whoever they ask.
Do AI notetakers support data residency requirements?
Some do, and the honest answer separates storage from processing. Vinyl keeps the lasting copy of every meeting on AWS in Sydney. Recording and speech to text are processed in the United States and speaker separation in the European Union, and those providers return their results to Australia and delete their working copies within 30 days. If your firm or your clients need data to stay in one country end to end, ask every vendor that question in writing before you start. Tax practices weighing this up can see how Vinyl works for tax practices, and UK practices can read our guide to AI notetakers for UK accountants.
What does a firm’s security questionnaire ask an AI notetaker?
Most questionnaires cover the same ground: how data is encrypted, where it is stored, how long it is kept and how it is deleted, whether it is used to train AI models, and who at the vendor can see it. Ask every vendor to name the standard, not just say “bank-grade security”, and to point you to where it is written down. Vinyl encrypts data in transit with TLS 1.2+ and at rest with AES-256, and keeps the lasting copy of every meeting on AWS in Sydney. Its answers to the rest are in the Privacy & Security FAQ.
How long does an AI notetaker keep client meetings, and how are they deleted?
Ask how long data is kept while you’re a customer, what happens when you delete one meeting, and what happens when you leave. Vinyl keeps meeting records for up to seven years by default, or less if your firm asks, and you can delete a meeting whenever you like or ask Vinyl to delete your firm’s records sooner. If you leave, you choose a full copy of your data in a standard format, deletion, or both, and Vinyl confirms in writing once it’s done. Backups age out within 30 days, and the providers that record and transcribe meetings delete their working copies within 30 days. With any vendor, also ask how long backups and AI providers keep their copies, and get the answer in writing.
Can we get a vendor’s promise not to train AI on our meetings in writing?
You should, because a security questionnaire needs more than a yes on a sales call. Ask whether recordings, transcripts and summaries are used to train AI models, and where that is written. Vinyl doesn’t train models on your meetings, its contracts require every provider it uses to make the same promise, and clause 4.10 of its Data Processing Agreement puts this in writing. Firms can ask for a copy of the agreement, and the Privacy & Security FAQ says the same.
Can the vendor’s own staff see our client meetings?
Questionnaires usually ask who at the vendor can open your content and which other companies process it. Vinyl staff only look at your content when you’ve asked for help, or when the law requires it, and every time a recording or transcript is opened, it’s written to a log that can’t be changed or deleted for seven years. Each provider Vinyl uses is bound by a written agreement at least as protective as Vinyl’s own, Vinyl gives at least 30 days’ notice before adding or replacing one, and it sends the full provider list on request. Ask any vendor for that list before you sign, not after.